Information Security
Basic Concept
With advances in digital technologies, the importance of information in corporate activities continues to grow.
Within the Tsubaki Group, ensuring information security is fundamental to maintaining the trust of customers and business partners, and we regard it as an important management issue that is directly linked to business continuity and the enhancement of corporate value.
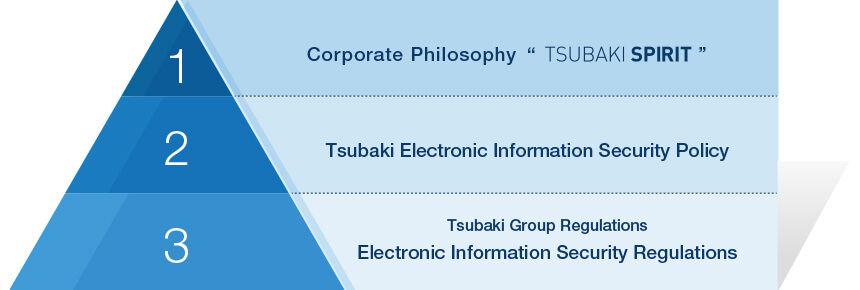
To ensure the confidentiality, integrity, and availability of information, our Group established the “Electronic Information Security Policy” in 2020 and applies it as a common global standard. With the Group head office taking the lead, we are promoting continuous improvement by monitoring the status of initiatives at each site and increasing their visibility.
In addition, in order to respond to increasingly sophisticated cyberattacks in recent years, we are building a framework that, in addition to conventional defenses, emphasizes early detection and rapid response, as well as preparedness to ensure business continuity. At the same time, we are also working to develop an IT infrastructure that enables the secure use of data and to improve employees’ IT literacy, with the aim of creating a secure and trustworthy digital environment.
Electronic Information Security System Chart
Promotion System
The company established the IT Committee in 1997 and expanded the committee system to include domestic Group companies in 2002. Since 2014, we have held an annual Global IT Summit to promote Group-wide collaboration. In addition, Regional IT Leaders have been appointed to oversee information systems in overseas regions. As cybersecurity risks continue to grow, we are strengthening our global information security governance to ensure robust protection of the Group’s information assets.
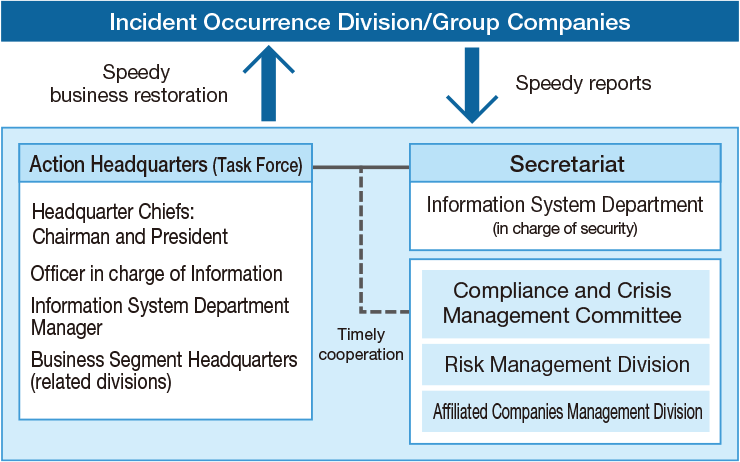
Our cybersecurity measures focus on three areas: preventing attacks, detecting them quickly, and restoring business operations as rapidly as possible after an incident. Among these, the most critical factor is the speed of business restoration in the event of a cyber incident. To support this, we have established a Cybersecurity Countermeasures System*1 headed by top management. Under this system, a team of experts, led by the Information Systems Department, can be quickly mobilized in accordance with our IT-BCP (Business Continuity Plan)*2.
*1 Cybersecurity Countermeasures System: An organizational framework for responding to cyberattacks and cybersecurity incidents
*2 IT-BCP: The part of the Business Continuity Plan that focuses on IT systems
Cyber Security Countermeasures System
Principal Initiatives
To strengthen security across the Tsubaki Group and ensure business continuity, we continuously implement integrated measures covering technical, physical, and human aspects of information security.
| Technical measures |
Building a secure and reliable IT infrastructure 1. Constantly monitor systems and networks to detect and respond to threats early 2. Protect important information assets through access management and secure use of the cloud 3. Develop backup and recovery frameworks to ensure business continuity in the event of cyberattacks or disasters |
|---|---|
| Physical measures |
Protection of critical assets 1. Implement access controls and monitoring for areas where critical equipment and servers are installed 2. Strengthen the secure storage of important data backups and disaster mitigation measures 3. Ensure stable operation through appropriate management and operation of IT infrastructure |
| Personnel security measures |
Strengthening IT literacy and organizational capabilities 1. Improve security awareness and response capabilities of all employees through continuous education and training 2. Reduce the risk of unauthorized use by ensuring awareness of security rules and properly managing accounts and privileges 3. Build an organization capable of responding promptly and appropriately by establishing systems and conducting training based on incident scenarios |